


Operational Fragmentation
Controls, risks, policies, and audits live across separate systems, and evidence must be consolidated manually.
Result: High operational effort and limited real visibility into risk exposure.

Multi-Framework Duplication
The same control must be documented multiple times across different frameworks and formats, creating constant repetitive work.
Result: Continuous workload and structural burnout within the security team.

Hard-to-Defend Risk
Isolated scoring, inconsistent methodologies, and weak links between controls and exposure make risk difficult to justify.
Result: Decisions that are difficult to justify to leadership and business stakeholders.

Disruptive Audits
Evidence must be gathered manually from multiple tools, interrupting operations and consuming critical resources.
Result: Recurring operational friction and loss of focus on strategic initiatives.
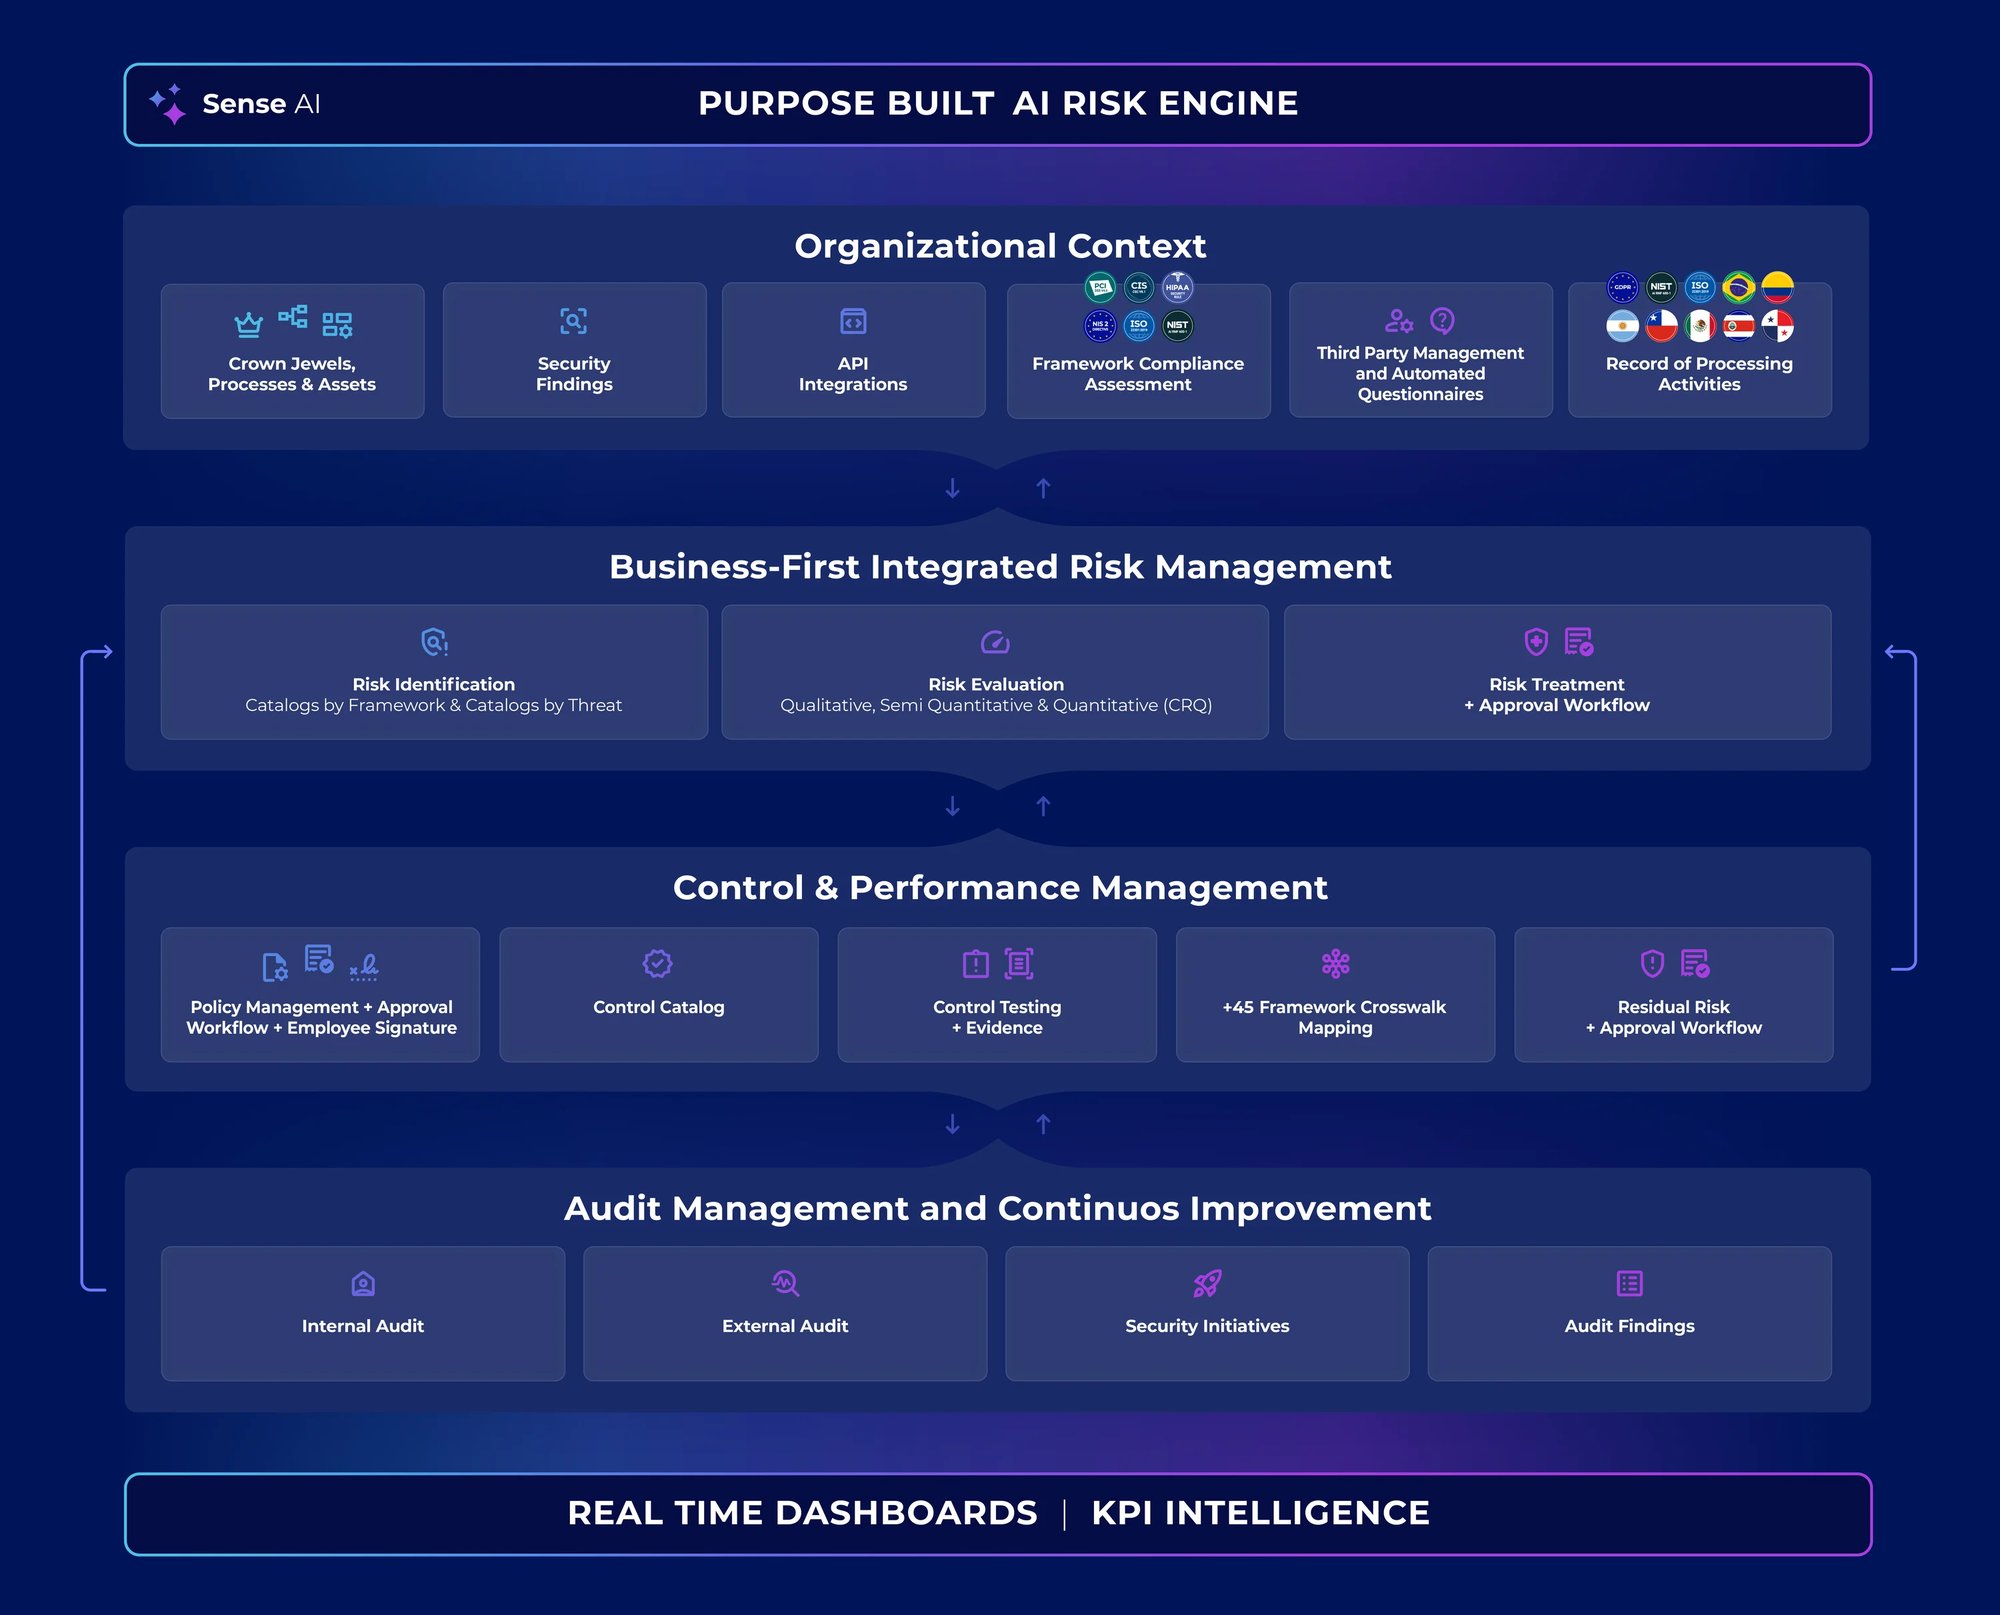
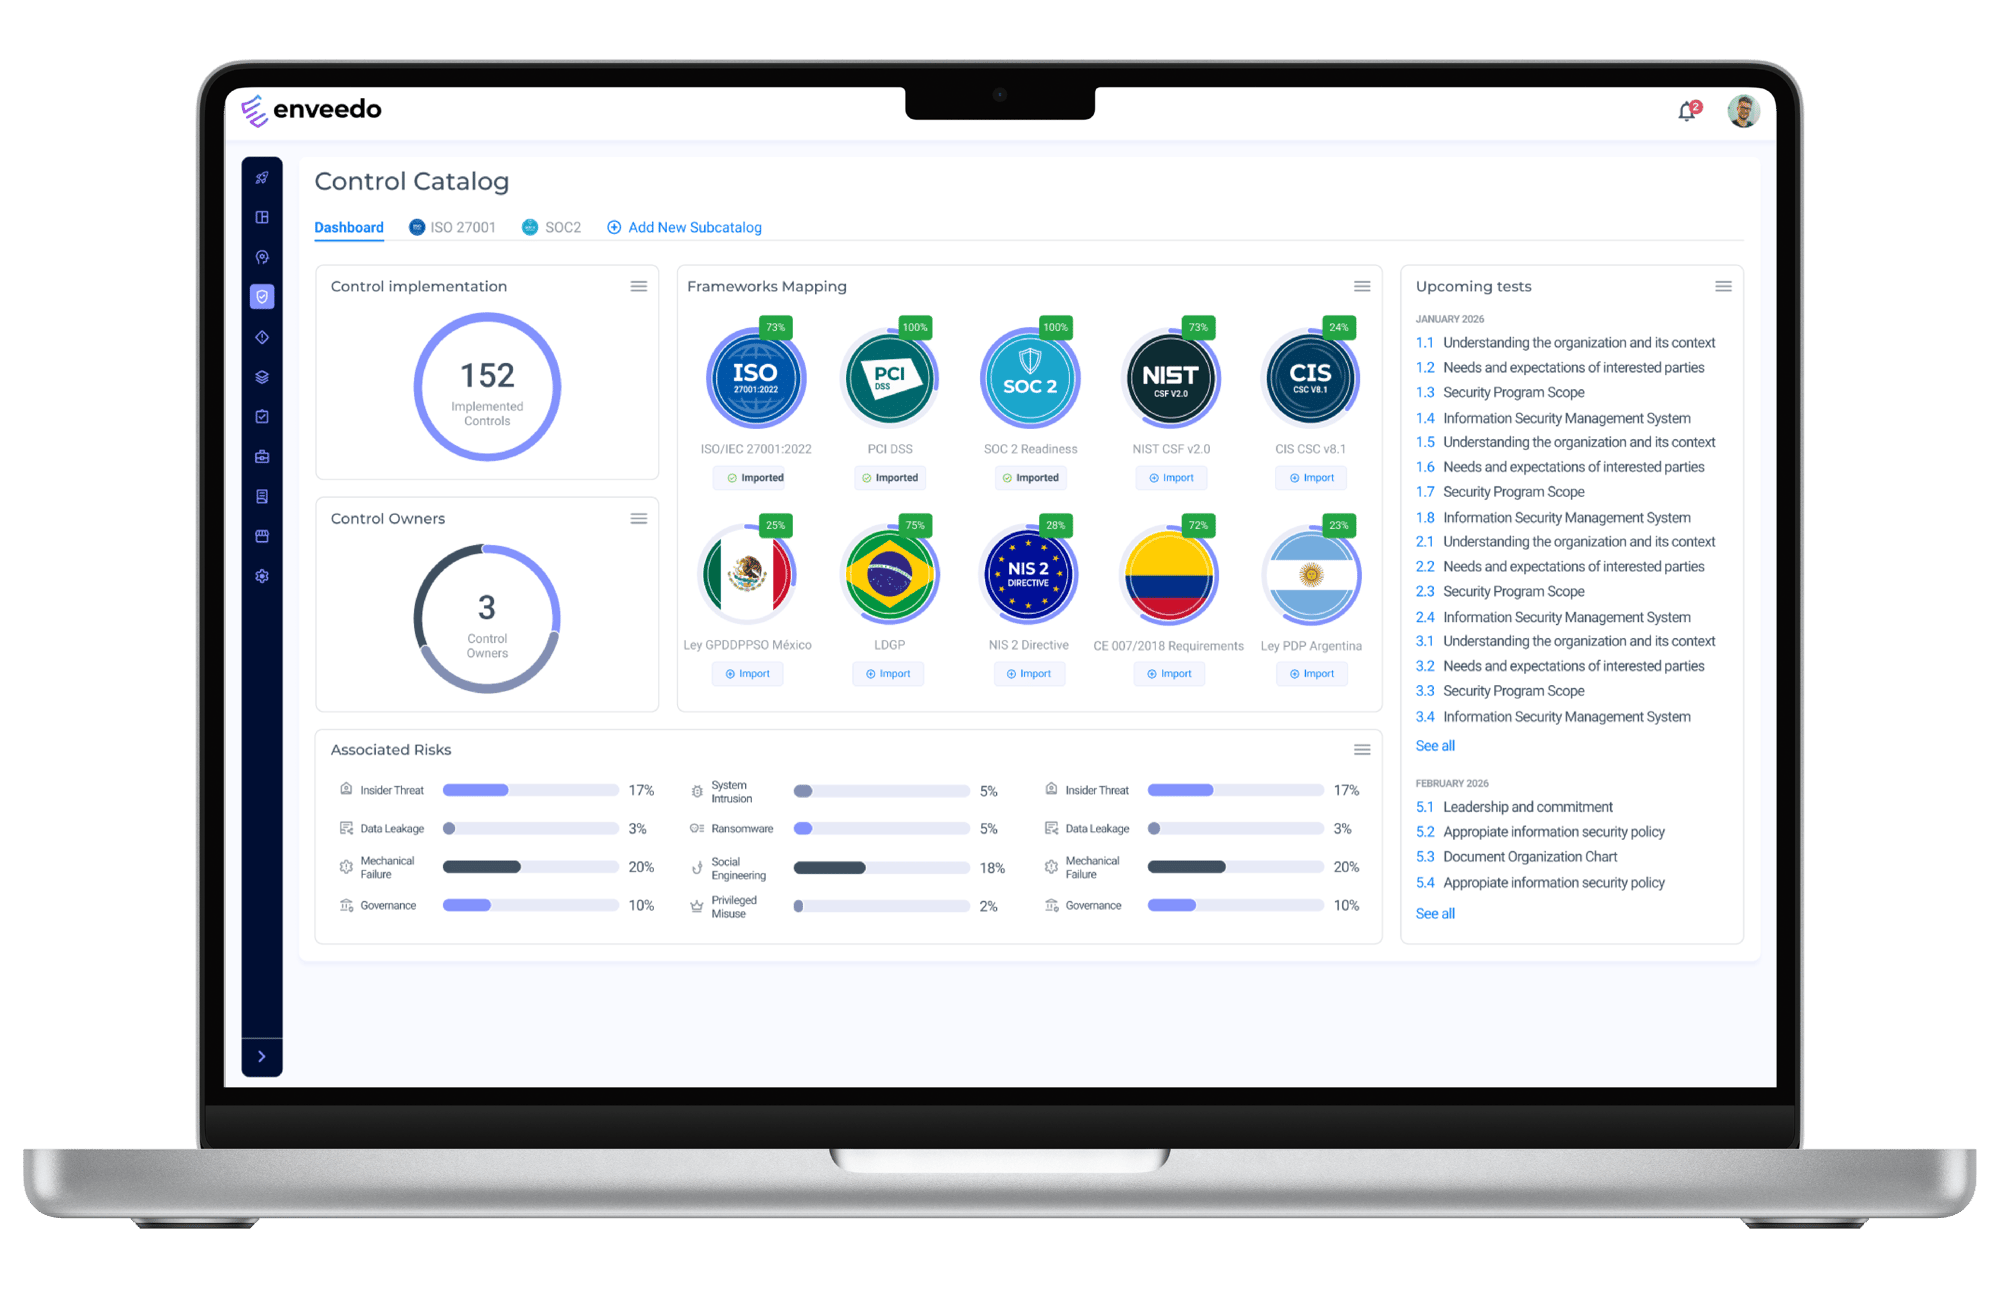
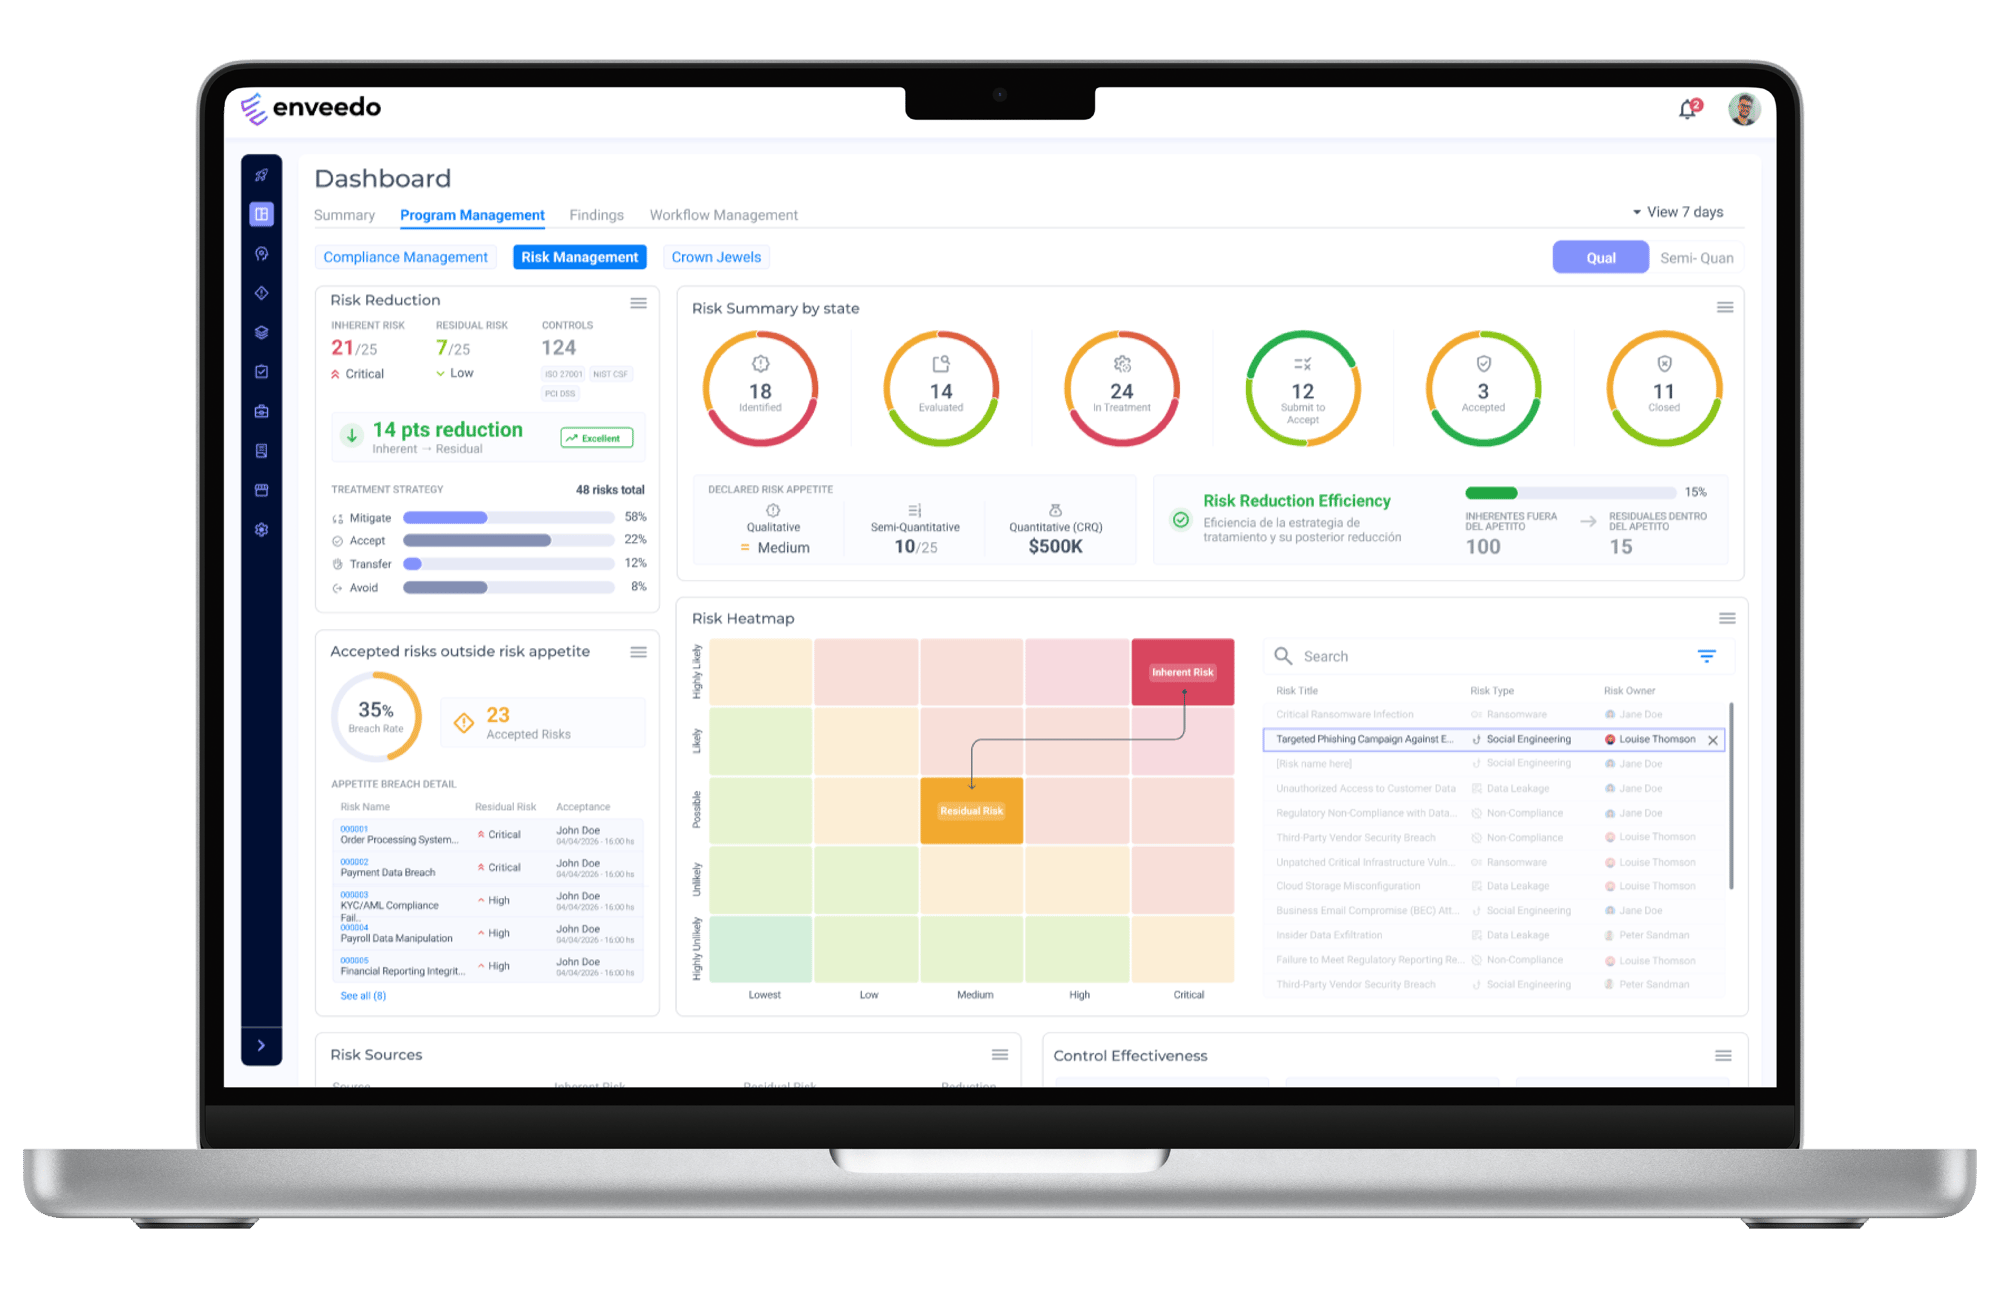

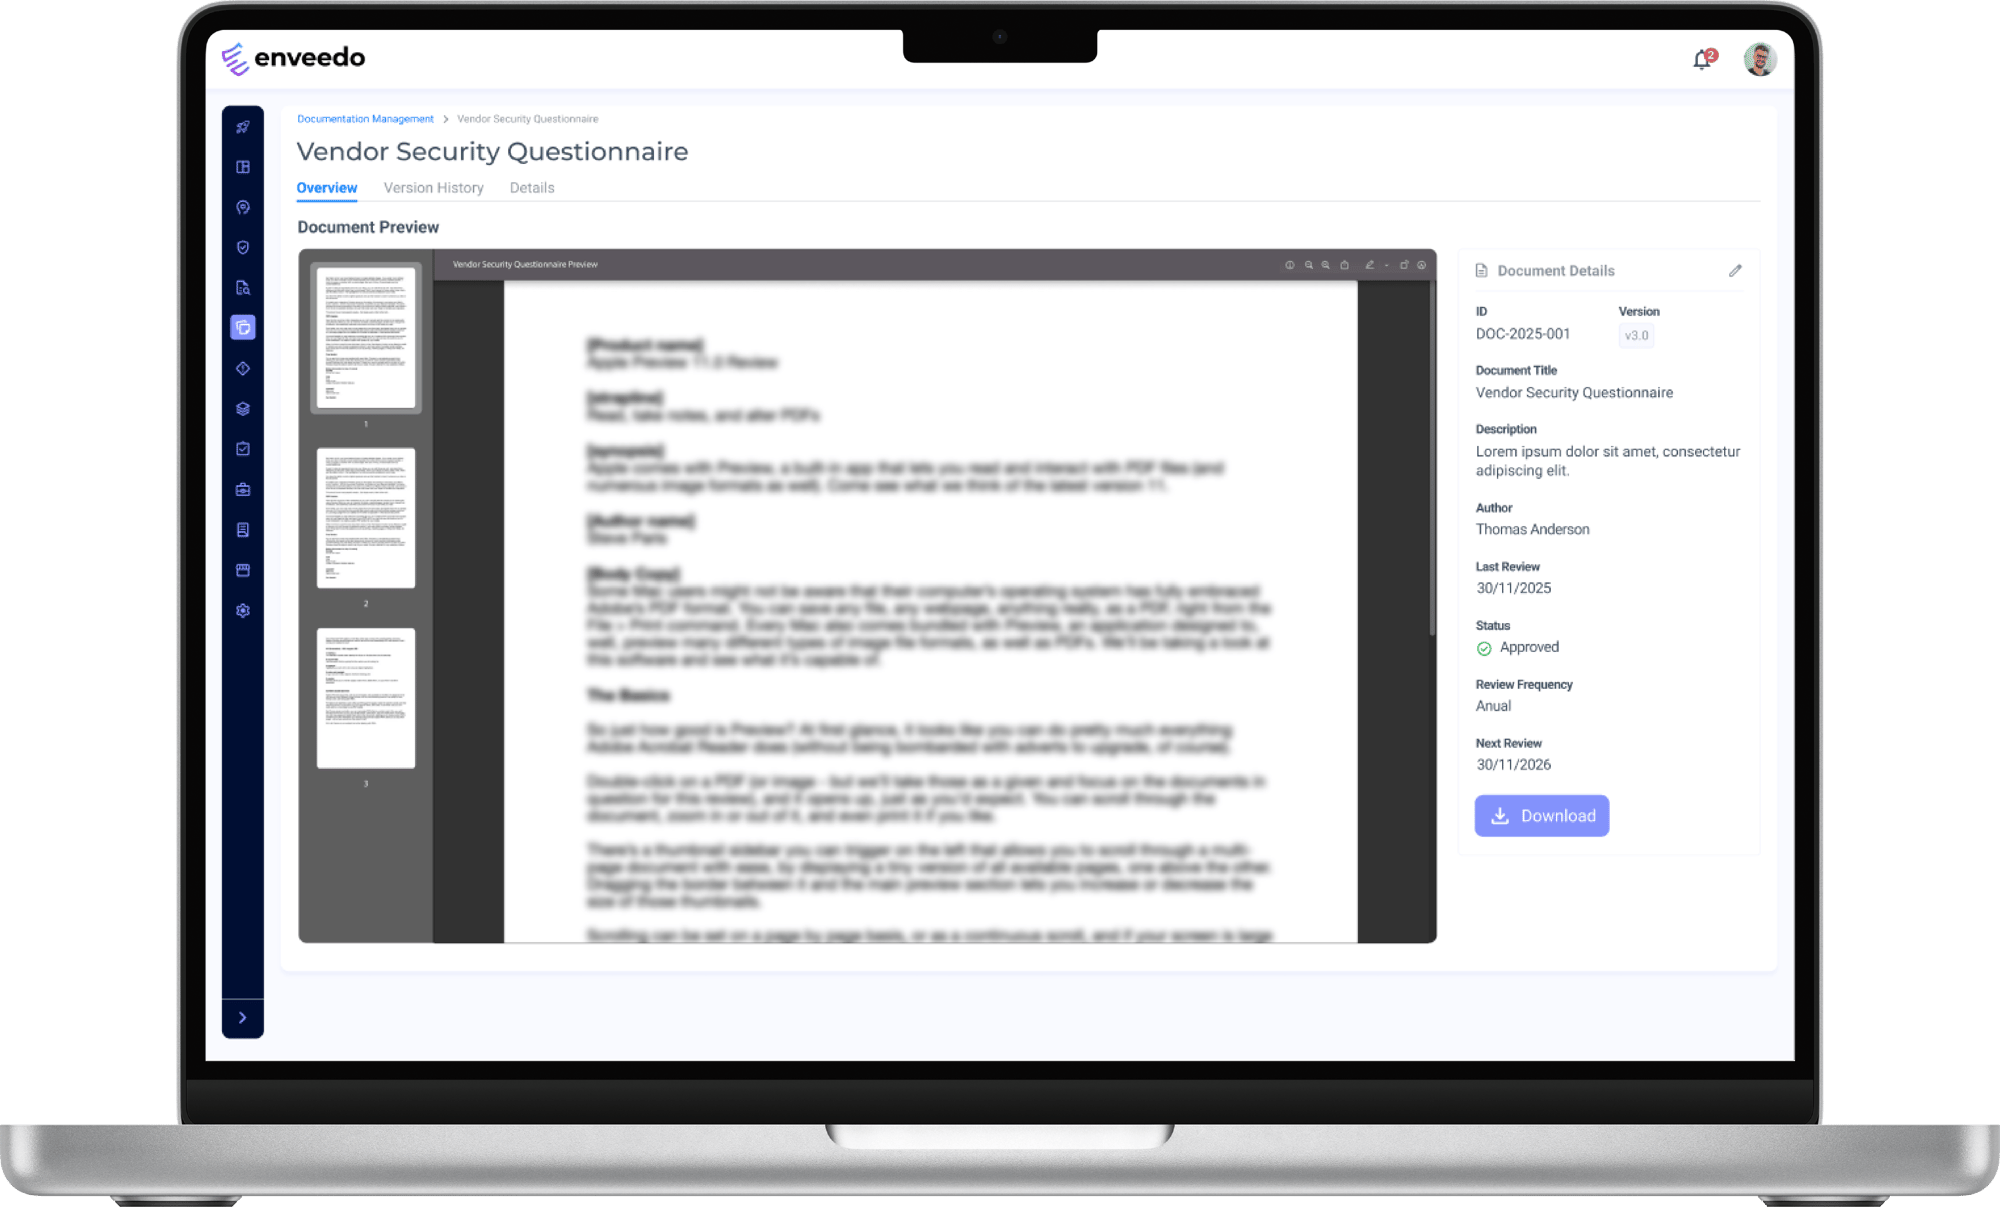
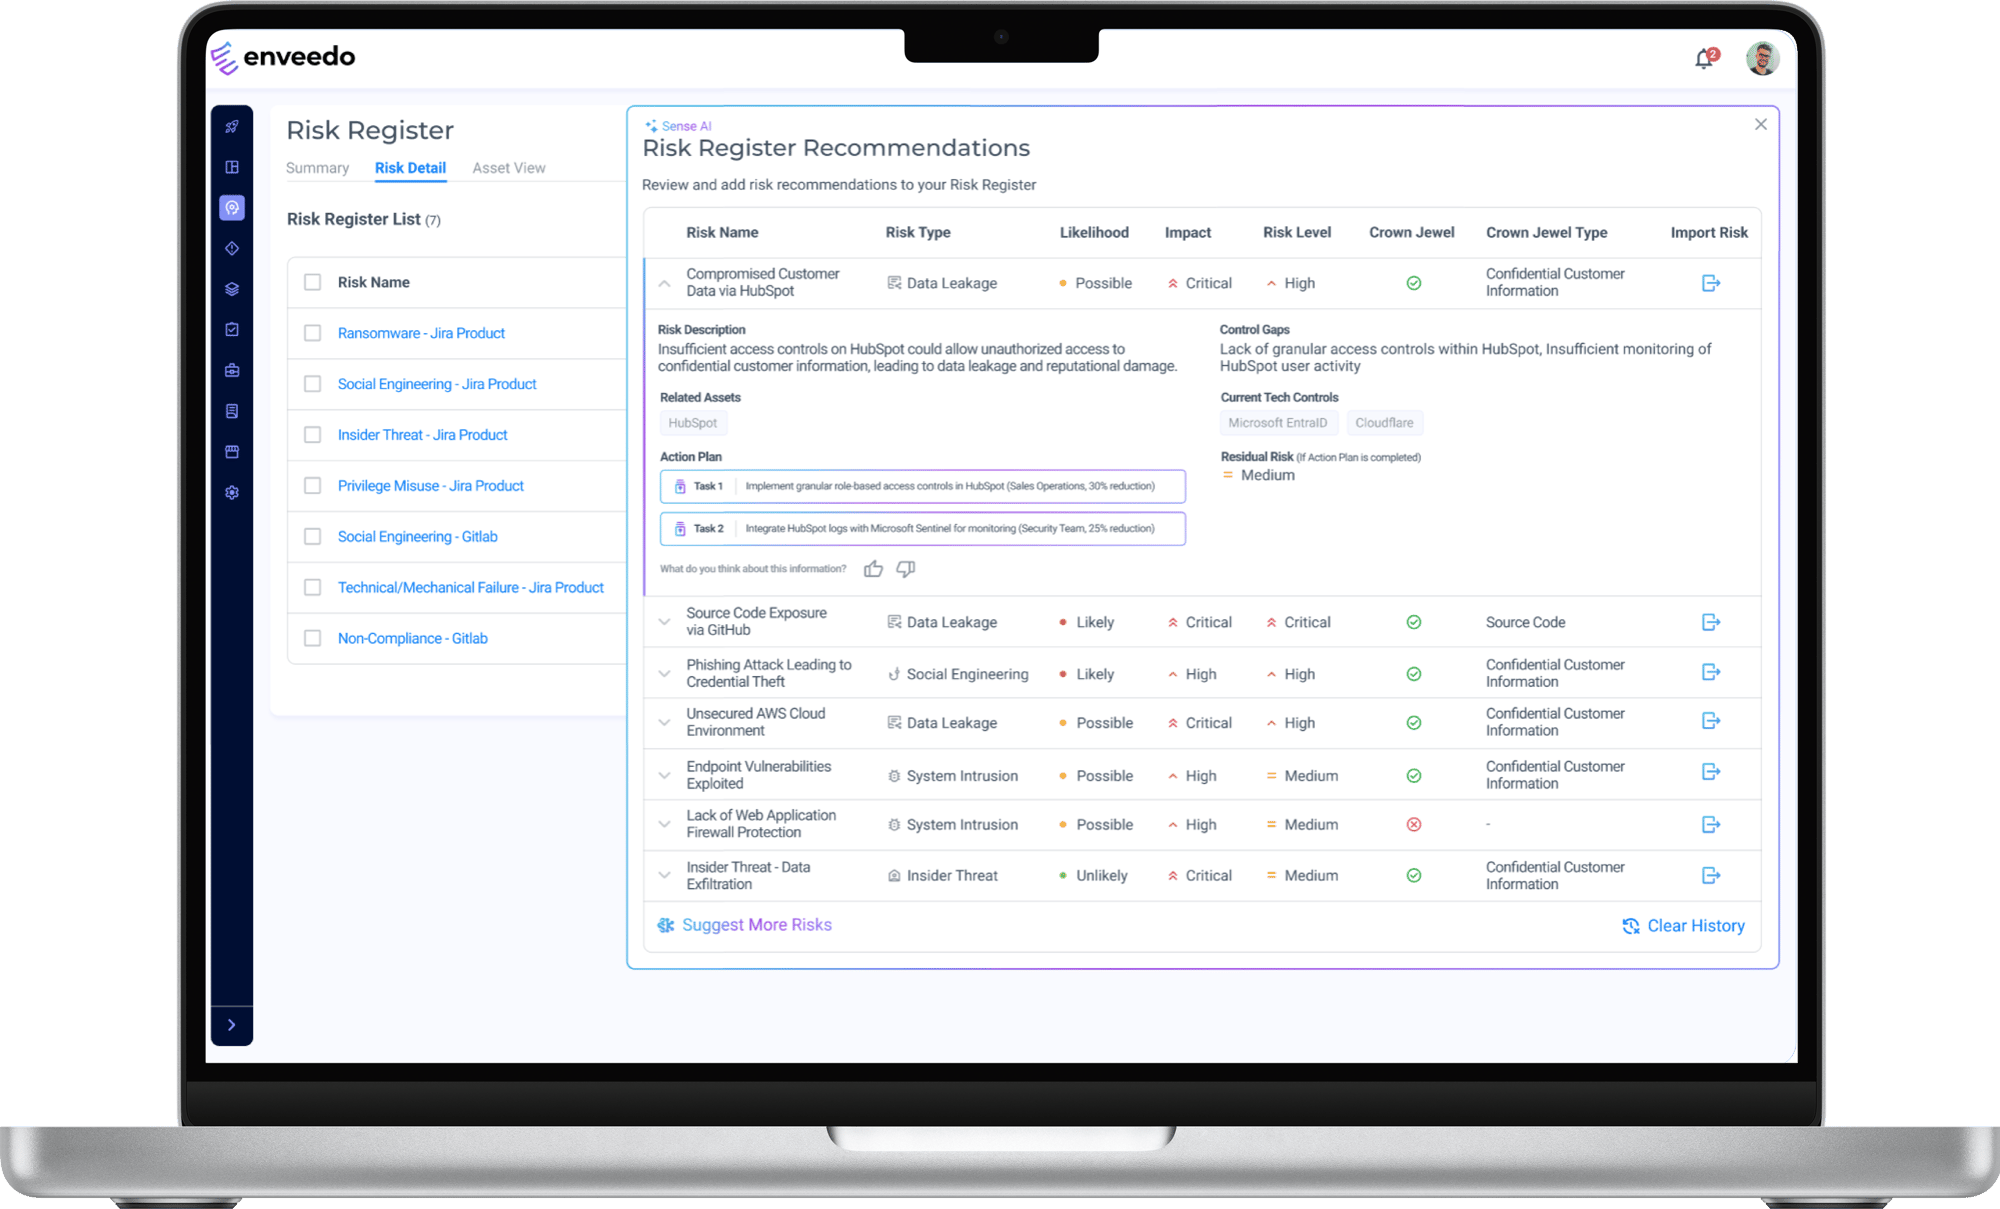
Let your organizational context work for you, not against you
- AI-powered risk suggestions based on your industry, assets, and declared processes
- Surfaces blind spots your team may have missed during risk identification
- Learns from your program structure to prioritize what matters most
- Only anonymized data is shared, your program details stay private
Outcome: faster, more complete risk identification without starting from a blank page every time.

Multi-framework environments

Cross-functional governance

Structural scalability

Distributed teams (CISO, Risk, Compliance, DPO, Audit)

End-to-end traceability

Integration with the existing technology ecosystem

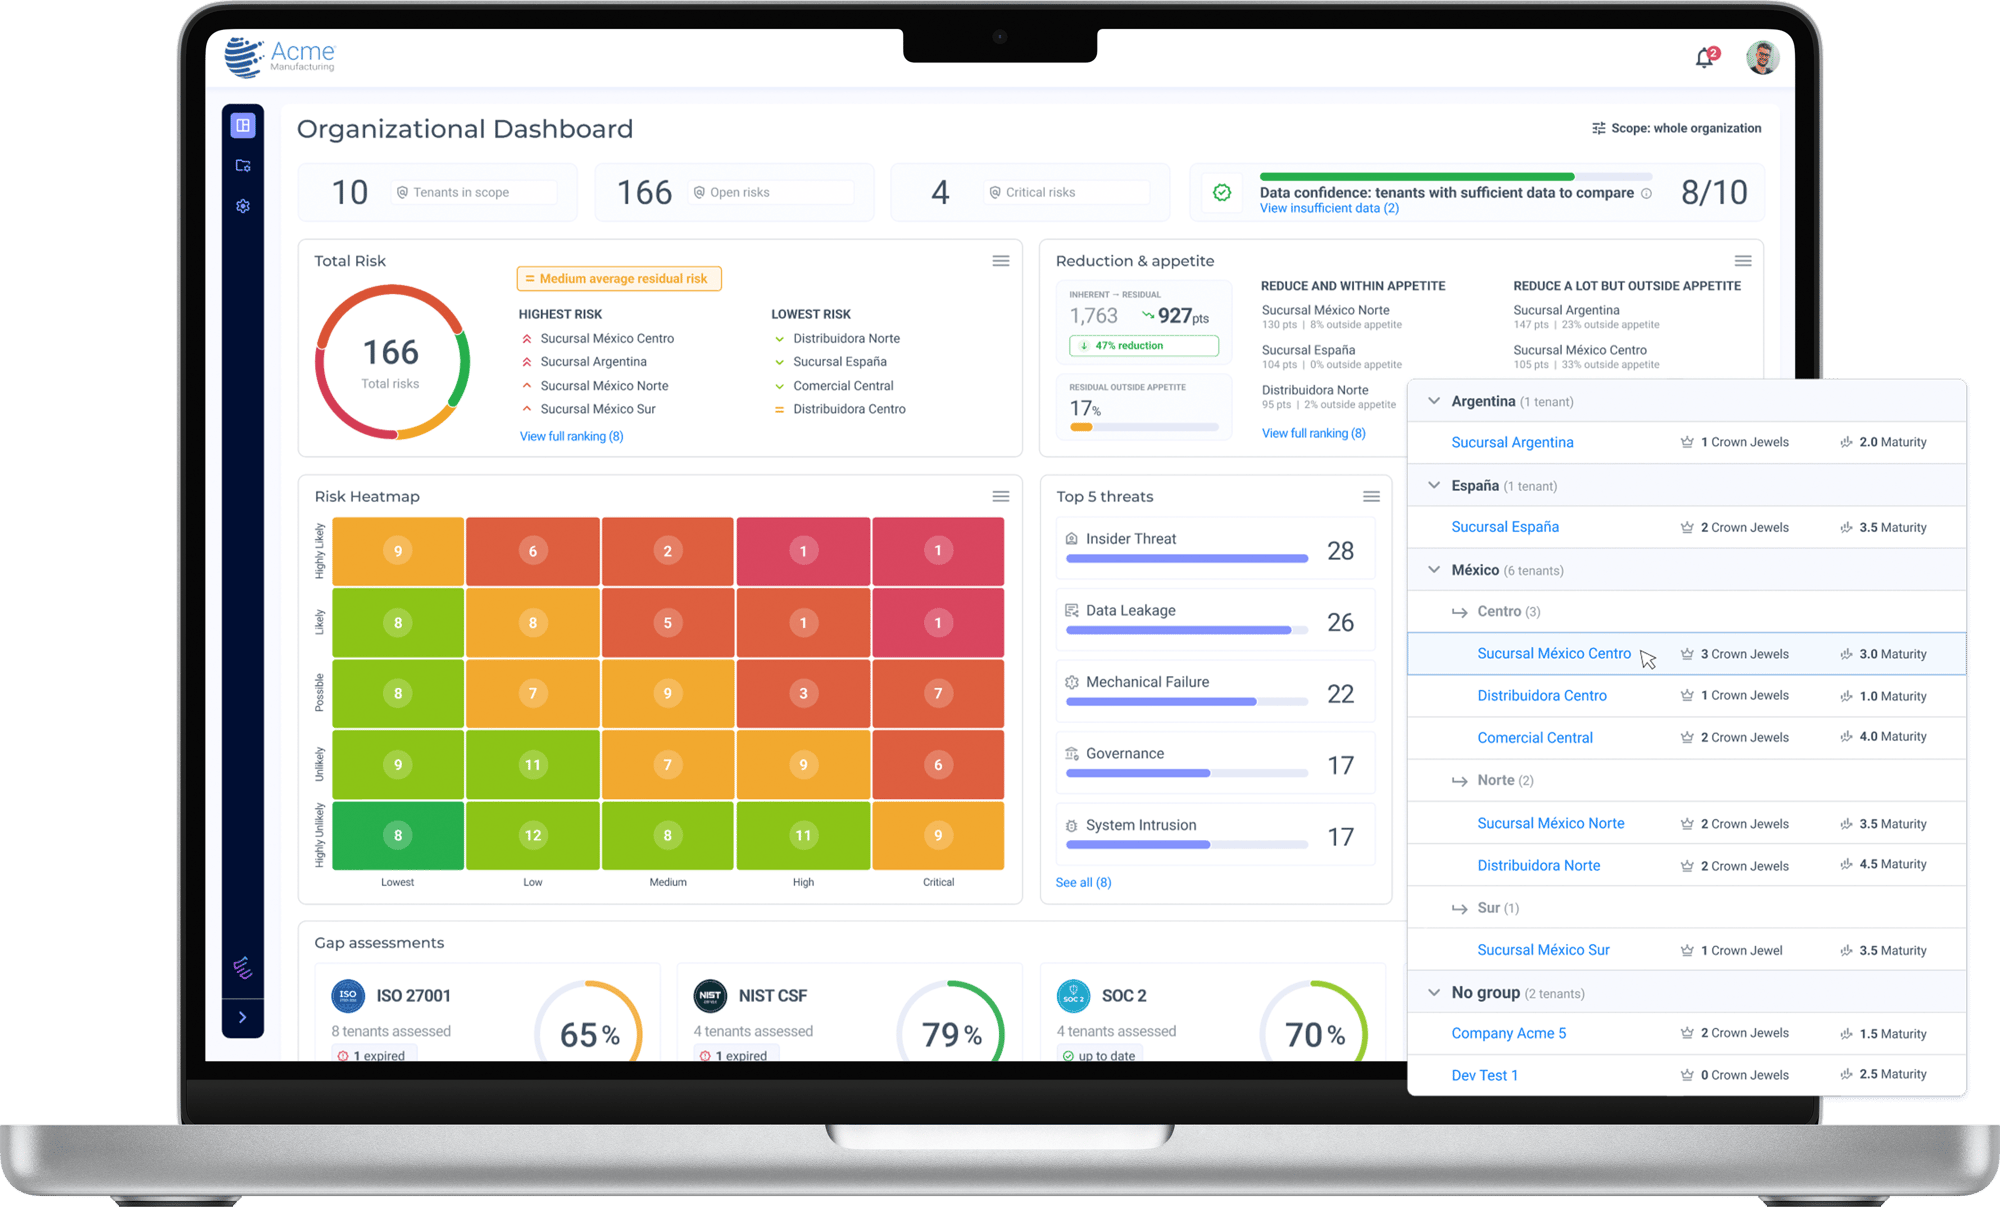
Exposure is reduced in a measurable way

Prioritization becomes strategic

Investment is justified with greater precision

Executive conversations become stronger

The program sustains performance over time